All work
Sentryline: Web Security Posture
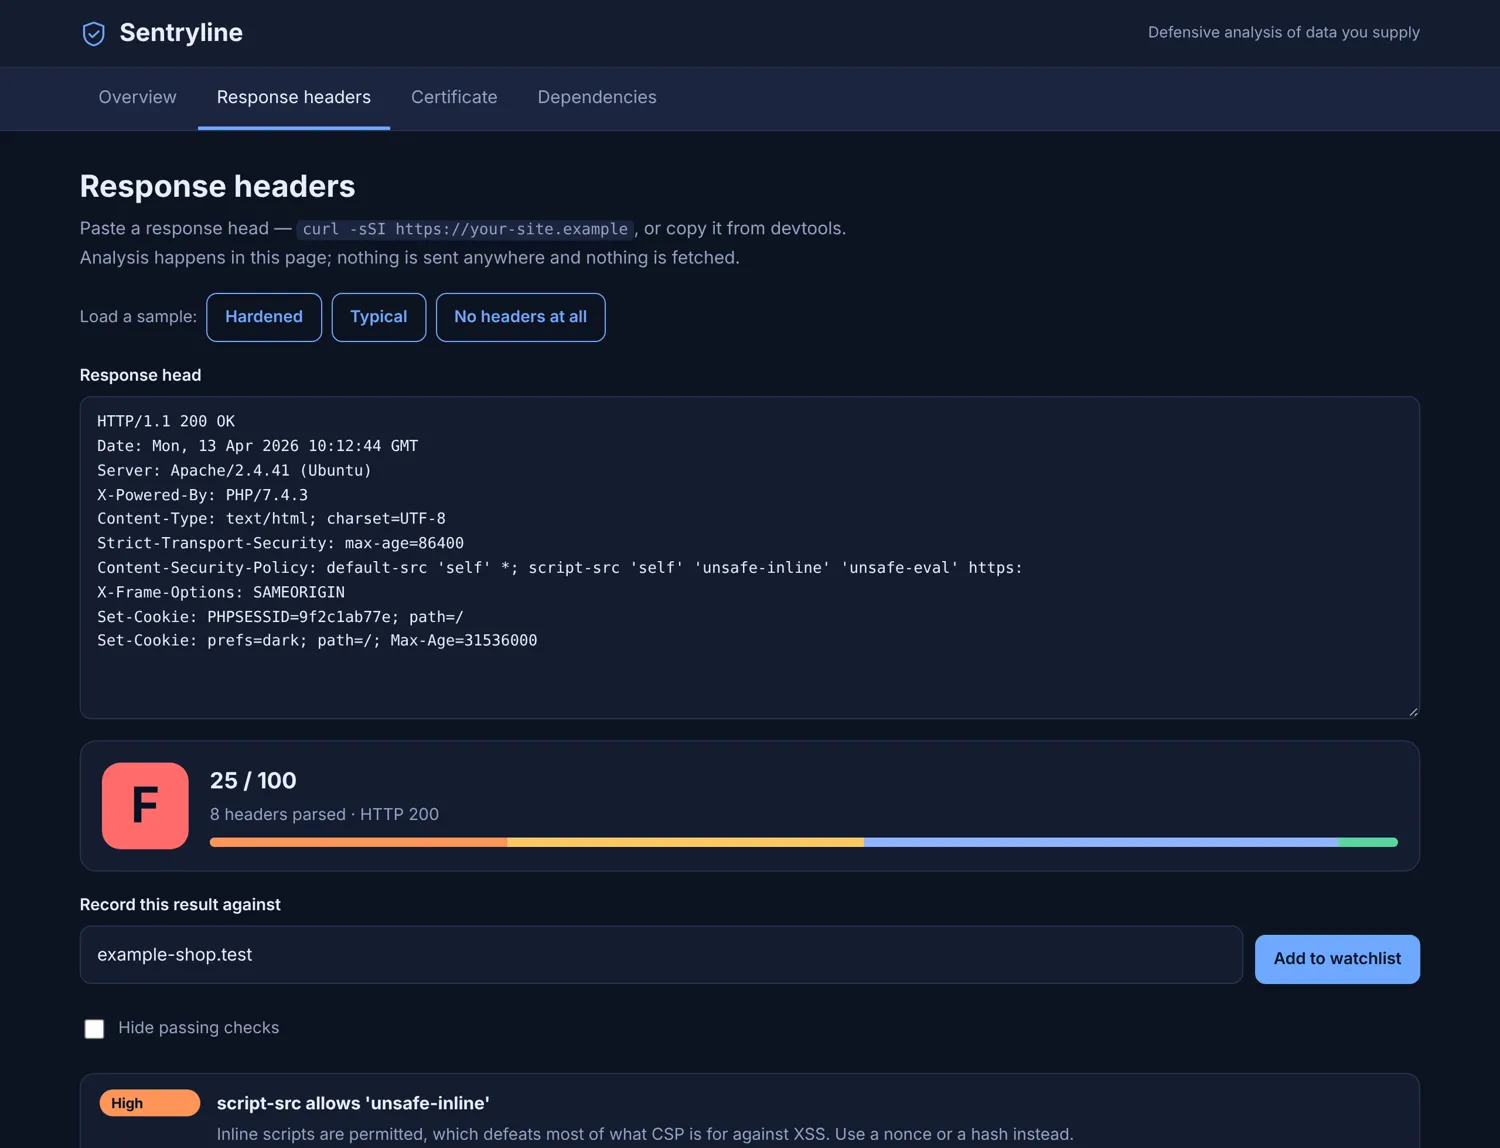
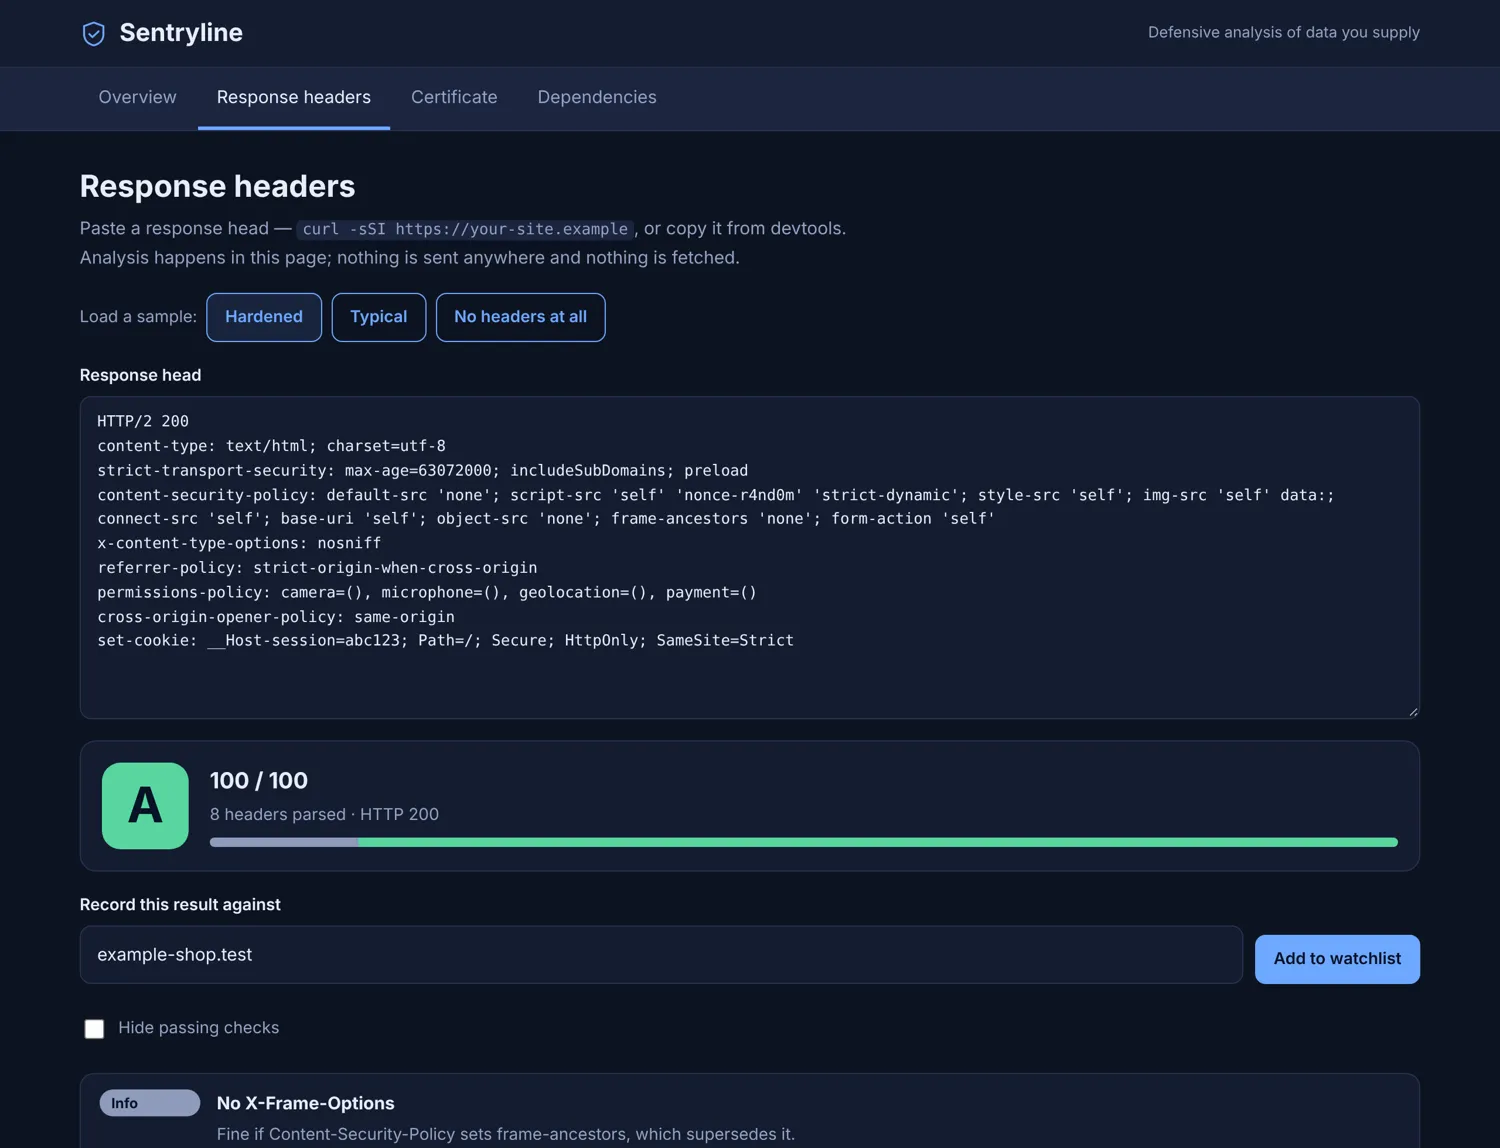
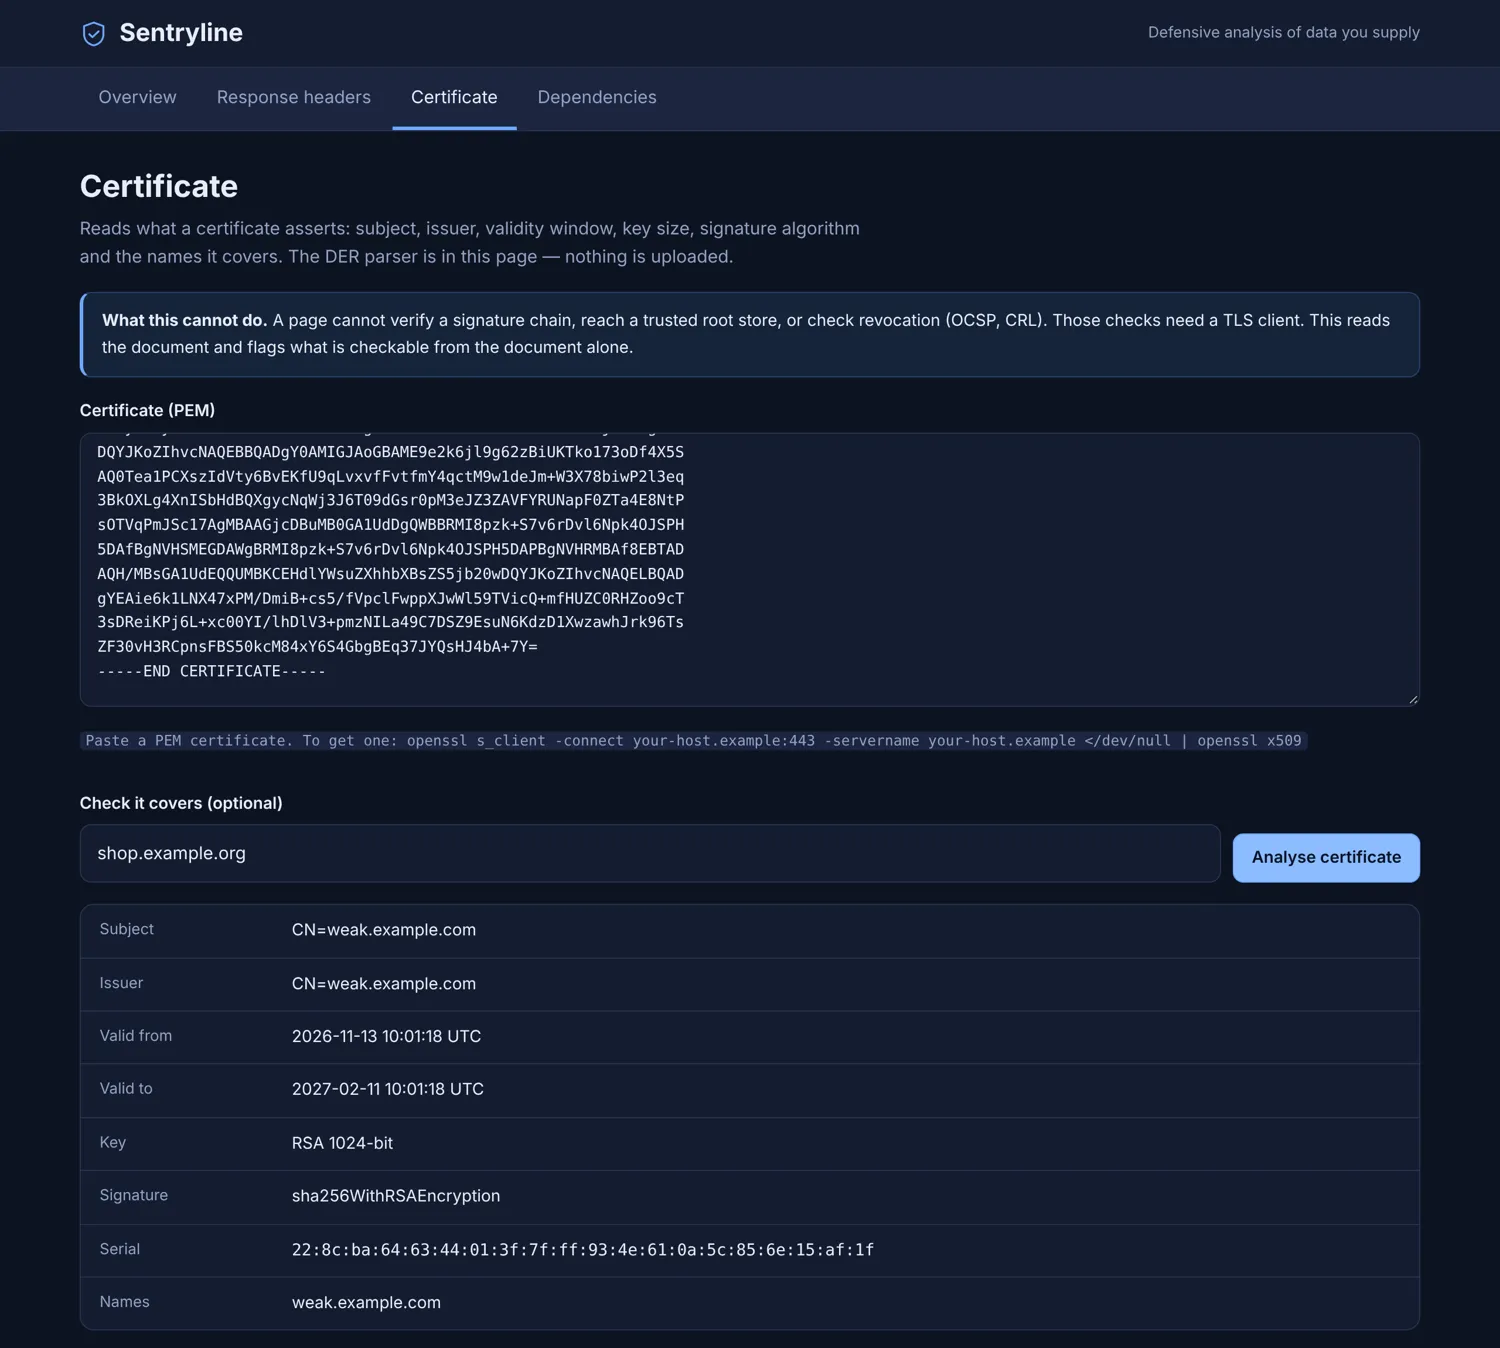
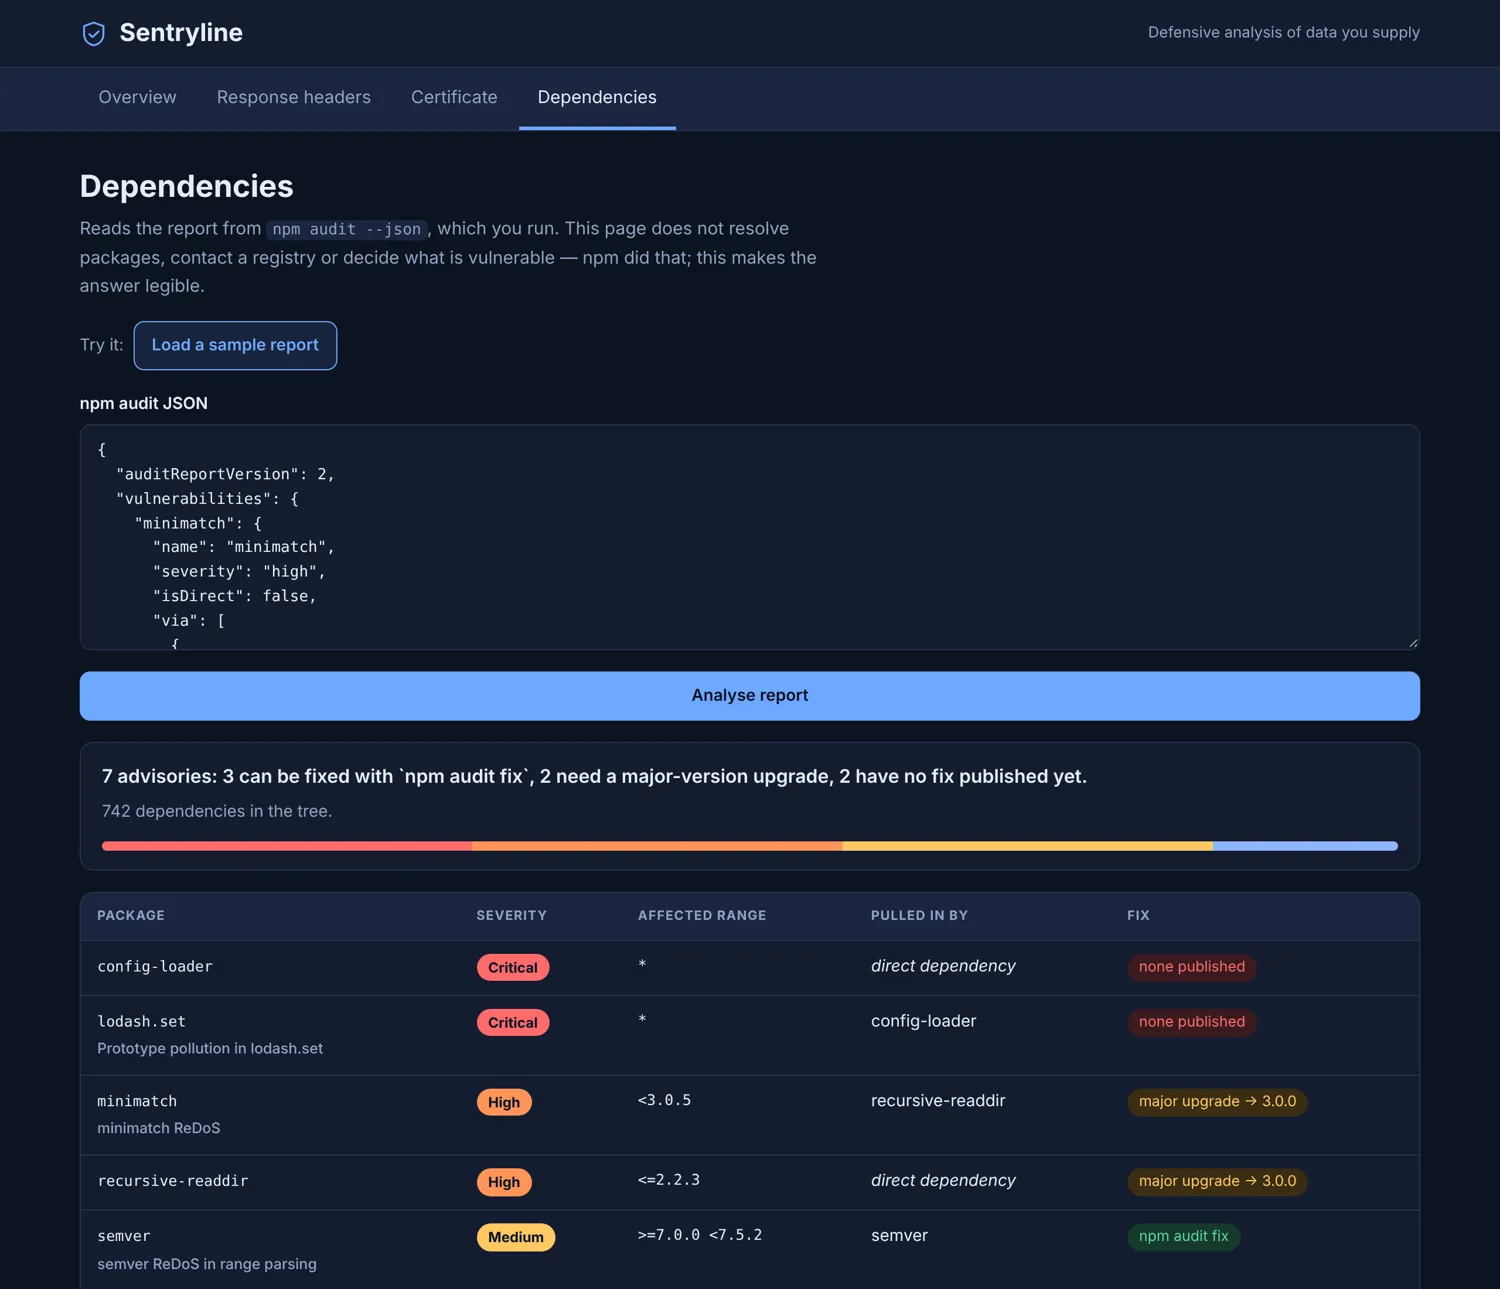
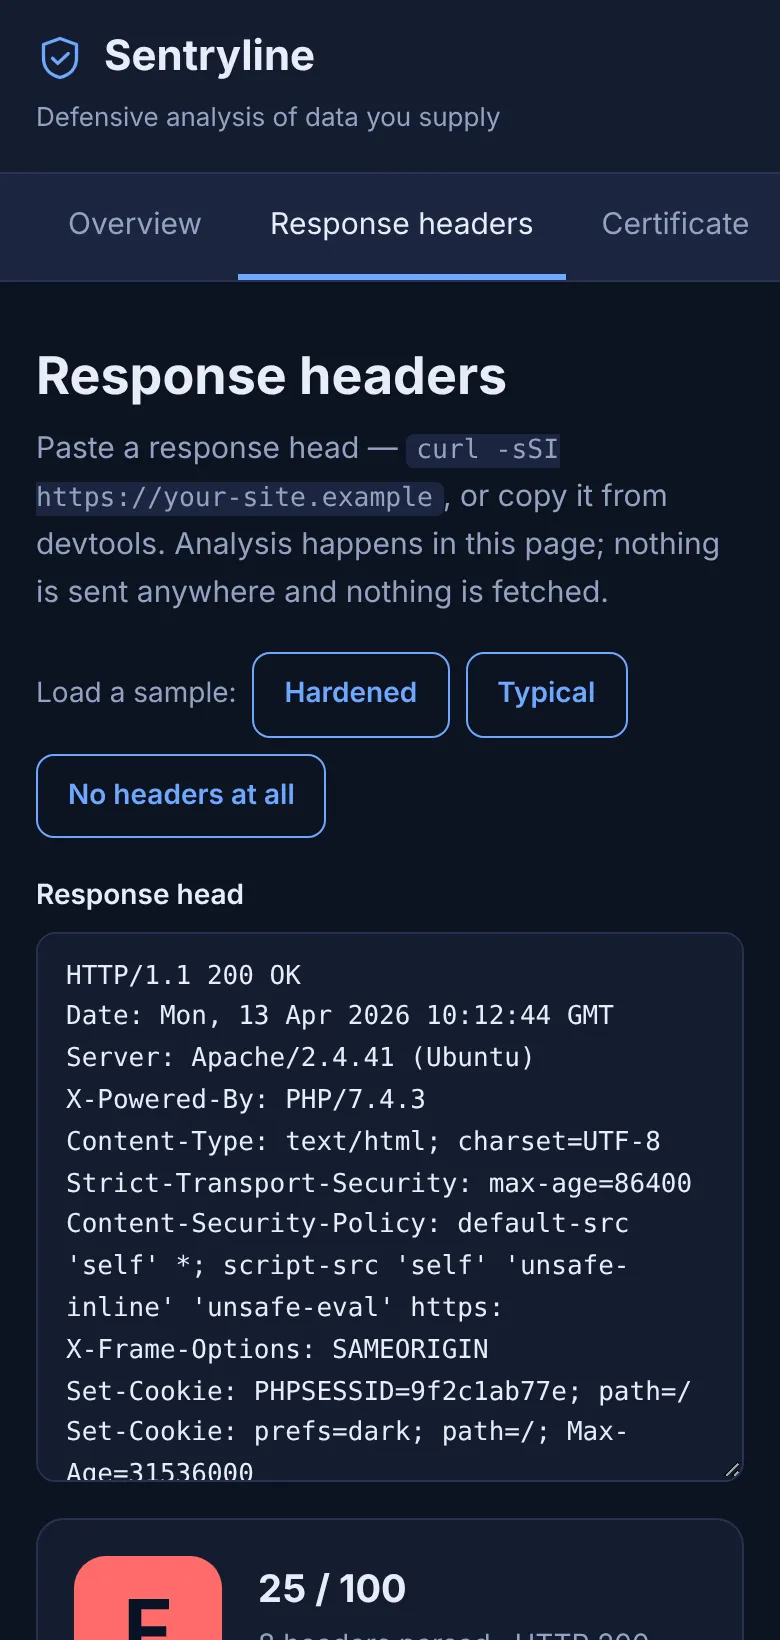
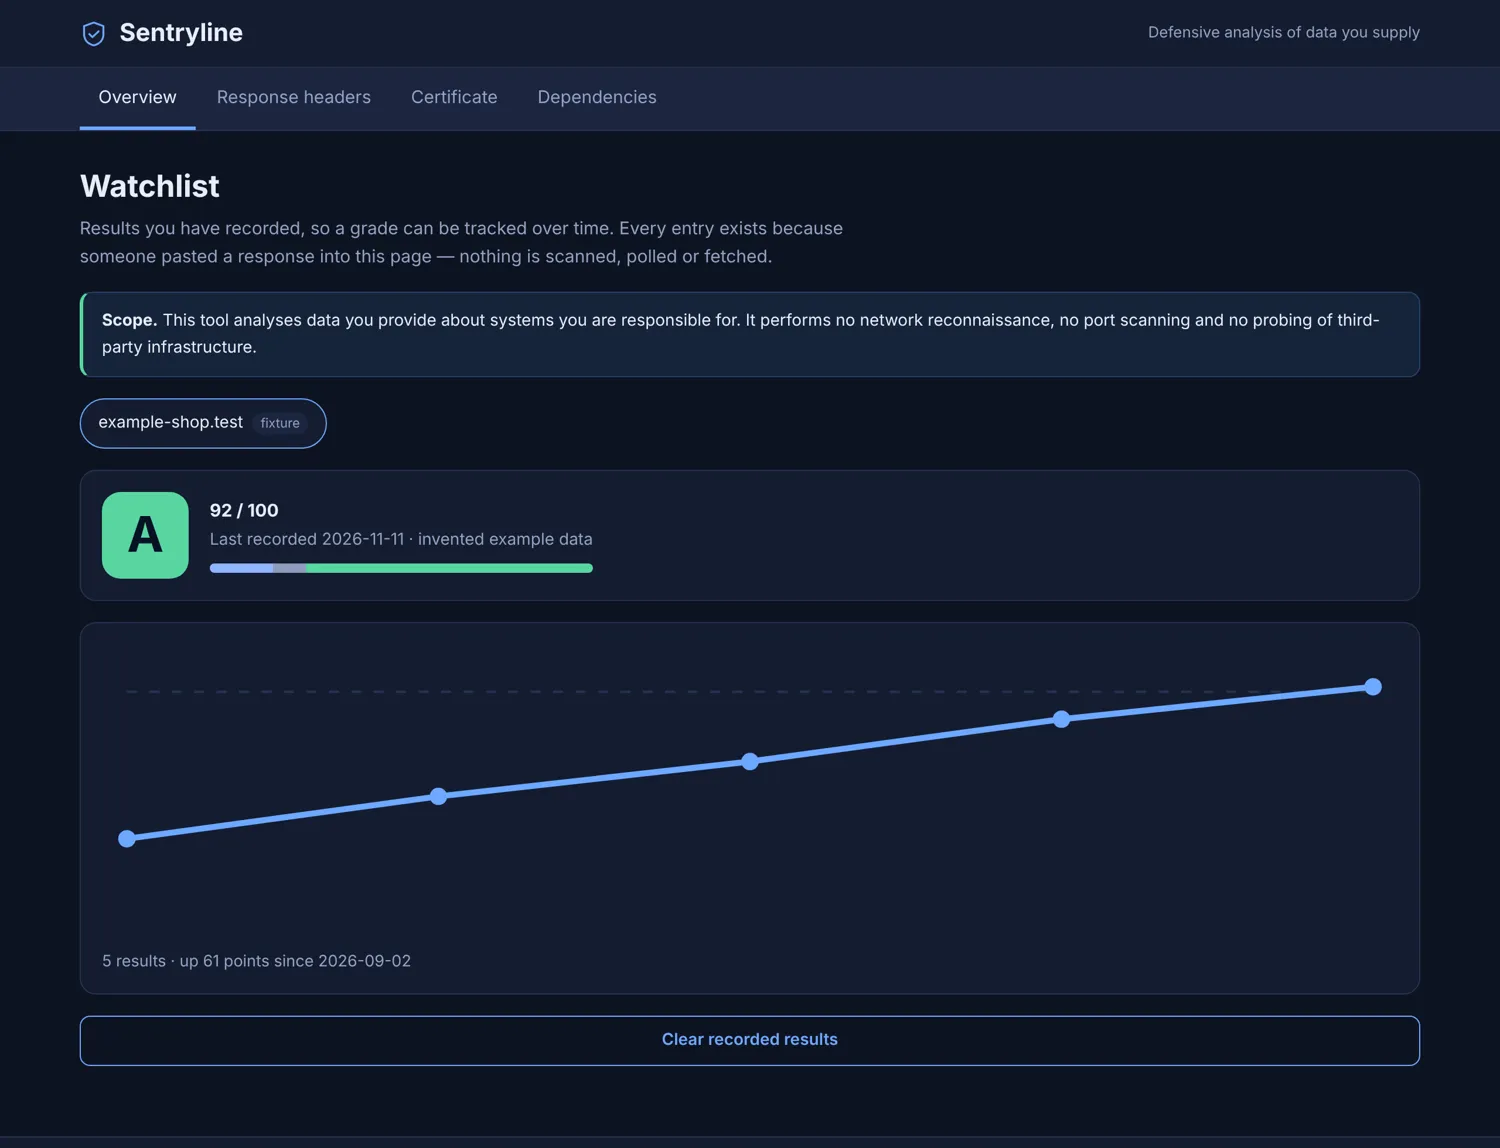
Defensive analysis of data you supply: security headers graded with reasoning, TLS certificates parsed by a DER parser written from the specification, and npm audit reports rolled up to the dependency you actually have to upgrade. It scans nothing.
This is a working demonstration, not a client engagement. The brand and data are fictional.
My role
Sole designer and developer
- Wrote the DER/ASN.1 parser and X.509 reader: subject, issuer, validity, key algorithm and size, signature algorithm, subjectAltName and basic constraints
- Verified the parser against openssl: the test suite asserts the subject, validity window and SAN list match `openssl x509` for eight generated certificates
- Built the header rule engine: CSP parsed directive by directive, HSTS, cookies, X-Frame-Options conflicts, wildcard CORS and version disclosure
- Implemented browser wildcard host matching, so *.example.com does not match a.b.example.com or the bare domain
- Built the npm audit reader, walking the effects chain to the direct dependency responsible
- Wrote 57 unit tests and 23 browser checks